

Today's health care organizations operate at the intersection of life-saving technology and escalating digital risk. From ransomware targeting patient records to state-sponsored actors exploiting medical device vulnerabilities, the cyber threat landscape is growing faster and more sophisticated, than ever before. And with artificial intelligence now embedded across clinical and operational workflows, the stakes have never been higher.
For this episode, we sit down with two seasoned cybersecurity experts from the WTW Cyber Risk Consulting team to break down what health care risk managers, frontline leaders and operational teams need to know right now:
- Why health care remains one of the most targeted sectors and what makes it uniquely vulnerable to opportunistic criminals and nation-state actors alike
- The dual role of AI in cybersecurity: how threat actors are weaponizing it to accelerate attacks, and how defenders can harness it for behavioral detection and faster response
- The risks of shadow AI and unsanctioned large language models creating new attack surfaces inside your own organization
- Practical steps to strengthen cyber resilience, from asset discovery and vulnerability management to third-party supply chain accountability
- How to speak the language of the C-suite and financially quantify cyber risk to secure the budget and organizational buy-in your security program requires
Joining host Joan Porcaro, Senior Vice President of Risk Services at WTW Healthcare, are Anthony Wilson, a former CIA and NSA intelligence professional and municipal CISO now leading cyber risk consulting at WTW and Omar Al-Shahery, a Senior Director on the WTW Cyber Risk Team with deep roots in FBI cyber threat intelligence and 22 years of defense intelligence experience.
Because in health care, security isn't about being perfect. It's about being intentional, staying informed and never standing still.
Transcript for this episode
ANTHONY WILSON: Those same AI tools that can identify unpatched software, software which has weaknesses that have not yet been corrected, that same AI tooling can help organizations, therefore identify those weaknesses and correct them.
SPEAKER: Welcome to the WTW podcast, Vital Signs, Risk and Insurance for Healthcare where we discuss the risk management and insurance trends and issues facing the US health care industry. We'll speak with our industry experts and clients in search of ways to improve your risk and insurance vital signs.
JOAN PORCARO: Welcome to the WTW Vital Signs Podcast. I'm Joan Porcaro, senior vice president of risk services for WTW health care. And I'm pleased to introduce a continuing episode in our newest podcast series entitled The AI Project, What Risk Managers Need to Know. A podcast series that explores the intersection of artificial intelligence, cybersecurity, and health care risks.
While lagging other industries for years, health care is steadily improving its security posture. But cyber attackers are also becoming more effective, too. This episode, Secure by Design, Cybersecurity Basics for Health Care, helps health care risk managers, frontline leaders and operational teams understand the evolving threat landscape in clear, accessible terms. First, I'd like to welcome our guests today. I'd like to introduce Anthony. Anthony Wilson, if you can go ahead and please introduce yourself.
ANTHONY WILSON: Thank you very much, Joan. Anthony Wilson with Willis Towers Watson cyber risk consulting team. Prior to that, I served as a municipal CISO for city government, led global delivery for a major cyber threat intelligence practice in the private sector. But majority of my professional career, several decades in the US intelligence community, CIA and NSA. Thank you, Joan. Happy to be here.
JOAN PORCARO: Thank you, Anthony. And Omar. Omar Al-Shahery.
OMAR AL-SHAHERY: Yes, my name is Omar Al-Shahery. I am a senior director consulting with the Willis Towers Watson cyber risk team. Before coming to Willis, I was with a major consulting firm that does cyber threat intelligence as a main delivery for clients. Before that, I was with the NCFTA that sits with the cyber division of the FBI for a few years. And 22 years of defense intelligence before that. Thank you for having us here, Joan.
JOAN PORCARO: Well, welcome to both of Anthony and Omar. So let's go ahead and get into our conversation. I'm going to start first with Omar. Are there any discernible trend lines for recent cyber attacks on health care organizations?
OMAR AL-SHAHERY: That's a very good question, Joan. Thank you very much. Actually, yes. What we have observed is really an uptick and increase in cyber attacks that are targeting health care organizations and health institutions in general. The reasons for that are the complexity of the systems used by these institutions. This exposes them to higher rate of failure for these systems and how they are integrated.
And also, these systems don't necessarily come from the same source. So they are sourced from different third party vendors. For example, the software that governs lab equipment or testing equipment or the databases used for clients or the payment methods, all of these are governed by the practices and controls of the initiator of the organization that created them, and they are being used for health care, but they are at the mercy of the third party diligence to do work properly.
What we have also observed is an increase in the rate of ransomware attacks. The main reason for that is the nature of the data that is held in possession with the health care institutions. These are very high value data like personal health information, personal health records, personal identification information, and financial information. All of that makes the health care institution a rather very tempting target for cyber threat criminals.
And last but not least, artificial intelligence, and both as a malicious tool in the hands of cyber threat criminals, but also as a point of exposure when it is used by the health institution to provide services or to provide certain efficiencies within the services provided to patients and partners.
JOAN PORCARO: Thank you, Omar. I'm going to jump over to Anthony now. Anthony, what is unique to health care that makes it an attractive target for cyber risks?
ANTHONY WILSON: Well, thank you, Joan. Again, another good question. I'll touch upon a couple of things that Omar mentioned, but expand upon them a little bit. First of all, the majority of cyber attacks on health care organizations are committed by what I would call opportunistic criminals looking for easy victims.
Put another way, or using the analogy of a herd of elk stalked by a pack of wild wolves. The wolves are not looking for the big, strong bull elk at the front of the herd with the huge rack of dangerous antlers. They're looking for the weak, sickly, elderly elk trailing the herd at the rear. And, I'm sorry to have to put it in those terms, but part of the reason for that is historically, health care organizations have underfunded their security controls.
And there are a host of reasons for that. Huge number of nonprofit health care organizations, hospital networks, but also even with for profit health care organizations, just working on very thin profit margins and having competing priorities in terms of where treasurers and financial officers invest in the organization.
The second issue that makes health care organizations so attractive to cyber criminals is-- and Omar alluded to this, the leverage that the sensitive data, the personal health information or PHI that health care organizations hold on their patients, their medical care, their prescriptions, really sensitive information, gives cyber criminals a certain degree of leverage, both from the standpoint of the heavy regulation that health organizations have, by at least in the US, the Department of Health and Human Services, as well as the HIPAA Act that have some fairly significant penalty regimes if organizations fail to keep that patient data, that PHI secure.
Another thing that makes health care organizations attractive targets for cyber criminals is also a point of leverage in the sense that health care organizations, particularly hospital networks, basically deal with issues of life and death with patients. The medical devices, some of the diagnostic and treatment technologies that they use. If those aren't available, it could seriously impact or harm patients' health and safety.
And so, cyber criminals being able to disable or potentially make those that health care technology unavailable is, again, a point of leverage that they have over organizations. Finally, I've alluded, again, to how heavily regulated the industry is. And believe it or not, and we've seen this in other areas of regulatory compliance with cybersecurity. Cyber criminals are particularly the more sophisticated groups, are acutely aware of the penalty regimes that organizations face are the potential for class action lawsuits, and they will use that as leverage against an industry such as the health care industry.
JOAN PORCARO: So I'm going to throw another question out with regards to AI and its role. So what role, if any, does AI play in cyber attacks, either in the offense or the defense? Throw the question to either one of you.
ANTHONY WILSON: All right. Well, I'll take the first part of this. So Omar and I and the cybersecurity industry, we basically think about AI and its role in cybersecurity in a couple different ways. And Omar, again, briefly spoke to this during his response to the first question. But again, we think about it in three ways.
It's, one, a means by which cyber criminals are able to increase the efficiency and lethality and success rate of their attacks on organizations. Secondly, as what we call in the cybersecurity industry, an attack surface, the actual AI tools and large language models that organizations use in their everyday work.
Think of some of ambient AI that hospital systems or doctor's offices use or other uses of AI to increase the speed and efficiency of organizations delivery of services to clients and patients. These very tools are in and of themselves attack surfaces are targets for cyber criminals. Either so they can compromise them, cause them to hallucinate or manipulate the output from those models, or to deny organizations the use of the models, which can result in a interruption in delivery of services to clients and patients.
Another aspect of this problem and something we'll talk to a little bit in response to some other topics is the issue of shadow AI. And essentially, what shadow AI is, it is AI tooling or are large language models that have been unapproved or have not yet been approved by an organization. But well-meaning employees just eager to try out new tools may inadvertently and not maliciously, take sensitive data and ingest it into those AI models and inadvertently cause a leakage of sensitive data, thereby triggering possible regulatory penalties as well as even legal liability.
And this is a bigger issue than a lot of people realize, particularly as we're still only a couple years into the advent of generative AI, but with the coming of agentic AI, this will continue to be a problem or an issue that haunts organizations, which is why the issue of governance of AI models in an organization is so important.
Now, the third part of this is how AI can be used in the defense of an organization's IT networks and systems. So for that, I'll turn things over to Omar.
OMAR AL-SHAHERY: Yeah, thank you very much, Anthony. You covered it very nicely actually. Like Anthony mentioned, while AI can be used by cyber criminals to perfect their craftsmanship and skill sets, compensate for the lack of language skills when they are attacking via email lures, and stuff like that, AI also can be used in a defensive posture.
The way that we traditionally defend a network is what we call signature detection. And threat intelligence eventually percolates down to a number of what we call indicators of compromise. An analogy to that of these indicators of compromise, or the IOCs, is if you have a mailbox and that mailbox receives a number of mail from different sources, but you already know that certain mail sources are trusted, like governments, friends, bills, whatnot.
However, some of them are spam, just useless mail, and some of them is malicious that you don't really want to open. Could have a booby trapped mail or whatever. And you know, someone have told you that if you see this address, do not open that box, that package or that parcel. That's how signature detection works. And we know that if there is traffic going to certain IP addresses or certain servers or whatever is mentioned, then you really block it. And the way to block it is via firewall.
This is really a very simplistic view of how it works. Now, this used to work in the past very efficiently. However, as cybercriminal criminals really perfect their craftsmanship and their capabilities and evolve beyond what we now to be the trend or the norm, what we need is something that we call behavioral detection. And an example of that, I am now logged in onto my computer from a certain location. I live in Pittsburgh. I work in Pittsburgh, so the network administrator knows that my name is associated with that geography.
If I log out for any purpose for a lunch break, for a coffee break, or for a meeting in person, and log back 30 minutes later from San Francisco, well, that's a red flag. And if that happens quite frequently, about 50 times a minute, which threat actors can actually mimic, then what we need is that point is something that can work at machine speeds to detect those anomalies on the network.
This is what AI can do very efficiently that human eyes might miss. So it really-- and this is one example of behavioral detection. Another one is at 3:00 AM in the morning really heavy traffic. A lot of emails going out from a certain IP on the network. That's another problem that AI can actually detect. That is network defender who is fixated on an issue on the monitor might miss while this happens in the background. This is something that AI can detect and can actually eliminate as a threat.
This is what we call hardening in cyber defense and also hardening configuration, hardening rules, and enforcing these rules and raising the flag when these rules are not being followed to the letter. And this is what AI can do. However, there's a caveat. As Anthony mentioned, AI can hallucinate and can drift and generate erroneous results.
And you don't want your AI solution that is defending your network to tell you there are five different insider threat actors emailing competitors, or just sending a lot of information out of your network at a very weird hour of the night, while in fact, there isn't any. So you need a lot of guardrails and testing on AI and continuous monitoring on AI performance to be able to use it as a solution for cyber defense.
JOAN PORCARO: So clearly, cyber threats to health care, they're increasing. And now with AI becoming more common, whether well-intended or malicious, in purpose. It's really changing the landscape in ways that make having really fine tuned preparedness plans really important.
And I think equally important is to ensure that the risk management professional truly has the awareness that they need and a better understanding of the impact on the health care enterprise. So back to you, Omar, again. Why would a state sponsored group, attack a health care organization as what recently occurred with a US medical device manufacturer?
OMAR AL-SHAHERY: That's a very good question because it's really timely. What we have noticed that state-sponsored groups are among the well-funded ones, the most skilled ones, the ones that actually innovate and be able to outpace defenders and outpace law enforcement and the novel ways of attacks. And this kind of skill level really varies from the very high end with the Russians and the Chinese state sponsored groups down to the Iranians and then the Koreans and the Vietnamese and others.
These are arms of government. And they follow government mandates and policies, and they target enemies of that government for any set of reasons or purposes. The Iranians, for example, what we have noticed and you mentioned the Stryker incident, when Iranians get involved in kinetic operations, military operations, we have noticed in the past that their cyber arm of their intelligence services usually go to hiding, and they want to preserve that capability and have it away from the targeting that takes place.
However, there are some caveats to that also. What we have noticed that lately a lot of the Iranian proxy groups are carrying out some of those attacks, and these are cyber criminal groups that align themselves ideologically with the Iranian objectives. We have seen these events or similar events when the Ukraine-Russia war onset started. And we have really were able at that time to identify which cyber threat groups in the criminal cyber threat realm were aligning with which side.
And we are now seeing it again with the Iran conflict. However, there is an exception. Some of those Iranian well-funded groups, the more capable ones, can actually outsource what we call infrastructure and infrastructure is a set of-- if you recall what I mentioned about indicators of compromise. These are IP addresses, servers, even people to other geographic locations or obscure their own geographic locations beyond being able to be discovered or be penetrated.
These are the high end kind of genre of the Iranian state sponsored groups. And they do have the capacity to really impact health care in two ways. They have a very, really dangerous capability of attacking industrial control systems. And what we call industrial control systems can include operational technology and internet of things, anything from your printer to the surveillance camera to the thermometer that is connected to your network, to the CT scanning machine that can send results via network to any mapping system.
Anything that really is integrated into a hospital system, for example. They can really attack them by something that we call the programmable logic devices or controls. And they're very successful. And these are the same controls used basically in water purification and manufacturing. So we see Iranian groups are quite efficient and capable when attacking organizations that utilize such technology.
The other way that they are very capable is sending wipers. And that's really what happened with the Stryker incident. This is a repeat of a very old-- it's not the same technique, but it's a repeat of the objective of what they use as code. They were able to attack a large Saudi oil firm with a wiper.
And the wiper is a code that can actually go into your machine or your system or your network entirely and really just do destructive work, eliminate files, folders, operating system components, data repositories, you name it. Once it's unleashed, it can render an entire network useless and very hard to recover. So this is in a nutshell, what the Iranians are really capable of.
JOAN PORCARO: Yeah, so we really briefly touched upon preparedness. And Anthony, what practical steps can health organizations take to improve their cyber resilience?
ANTHONY WILSON: Sure, Joan. Obviously, time will not allow for discussion of the entire spectrum of actions that organizations can take to ensure their cyber resilience. But I want to hit upon three in particular, if I could, both because of their importance to any organization, but also their relevance to health care specifically.
So a big 50 cent word in the cybersecurity security industry is asset discovery or asset management. So basically what that is knowing what IT devices, software, things like AI models, et cetera are connected to your network and resident in your IT environment. This may seem to some, in the audience, a fairly straightforward thing.
I can assure you it is not for large variated organizations, particularly organizations which have a variety of subordinate facilities, maybe in different geographies, different departments. I can tell you that at one point, serving in a cybersecurity role, we integrated a new asset management, asset discovery tool, and we were shocked at some of the things that were connected to our network and shocked in a bad way. And I'll explain about this a little bit more.
So knowing what we call-- what IT assets, devices, software, et cetera are resonant in your network. And this is the big important caveat, knowing what their condition is. Condition because in particular, we talked the last question about AI. Well, AI has increased the speed at which software vulnerabilities can be identified and exploited by malicious actors.
Now, the flip side of that is that those same AI tools that can identify unpatched software, software which has weaknesses that have not yet been corrected, that same AI tooling can help organizations therefore identify those weaknesses and correct them. Secure those weaknesses. But the problem is when threat actors, cyber threat actors get their hands on these tools, they are moving at a rapid pace to identify those weaknesses and instantly exploit them.
And AI has made the exploitation of those software weaknesses or vulnerabilities much faster. It used to be that cyber threat groups would take weeks or months develop the malicious code to exploit a particular vulnerability. Now with AI, they can do it in days or even hours. So, it becomes even more important for organizations to identify the IT assets resident in their network or their IT environment that are unsupported legacy assets.
That is the company which designed the software or the hardware tool that the firmware or software is being run on, no longer supports. It may not have put out any new updates or software patches on the product in years, in some cases. So it's just sitting there on your network waiting for a bad guy to find it and then exploit it. So that's number one, knowing what's in your environment and the condition of those assets.
Number two, third party attacks, represent something like over 40% of the way in which cyber threat actors go after organizations. They don't necessarily go after them directly in every instance, but they go after them via their third party vendors. Essentially, your supply chain. The organization that supplies your accounting software, that supplies the diagnostic equipment that you use in the ER.
You think of that famous case now 10 or more years ago, of a major retail chain in the US, which was taken down by the fact that a malicious actor accessed the company's HVAC or air conditioning vendor who just happened to be connected to the retail chain's own network, but tunneled their way through the AC vendors network, jumped over to the retail chains network, and took down some of their point of sale devices or compromised their point of sale devices, costing the company millions of dollars and some of their customers tons of money as well.
So holding the vendors in your supply chain to account for their own cybersecurity posture, whether via contractual language, whether via service level agreements, whether requiring that your vendors meet certain cybersecurity standards, external cybersecurity standards. And I'm thinking here of things like ISO or even things like FedRAMP, GovRAMP, the Department of War's CMMC certification.
All of these are various ways that you can hold your vendors to account for their cybersecurity posture to defend your own network and make sure that your supply chain isn't a pathway for malicious actors to get to you. And then finally, my third point is, one of the things that CISOs and infosec information security teams struggle with to obtain the type of budget spend that they need for their cybersecurity programs to get the approval for those budgets from the people that write the checks that make the decisions.
The chief financial officers, the treasurers, the city managers, et cetera is being able to communicate in meaningful terms just what the risk is. And I can tell you from having been a former CISO, it's not enough to tell your chief financial officer, hey, if we don't spend this additional money on this particular cybersecurity control or our tool, bad stuff will happen. Well, bad stuff will happen doesn't necessarily resonate with chief financial officers.
But what will resonate with them is if you're able to financially quantify that cyber risk in terms that are meaningful to the chief financial officer, like if we don't implement this particular cybersecurity control or buy this particular cybersecurity tool, what can happen is we could face business revenue losses of $9 million, and we could face regulatory compliance and legal liability in excess of $20 million.
Well, all of a sudden, you've taken the conversation from something very abstract, bad stuff will happen to real dollars and cents that all of a sudden, it makes that $600,000 spend you want to make on the new cybersecurity control, it puts it in context. All of a sudden, when you're facing $29 million in potential losses, a $600,000 spend on a new cybersecurity control doesn't necessarily look like that bad a deal.
So anyway, those are our three general suggestions that I have. I could, of course, go on much further, but that's all I have to say on that question.
JOAN PORCARO: Well, thank you, Anthony. We're coming to a close in our episode today, and it's really clear to me that health care security isn't necessarily about being perfect. It's really about being intentional and being in a constant state of awareness of just the ever-growing risks that are out there.
And as defenses improve, our attackers get smarter. So really understanding the basics and building security into everyday decisions become more important than ever. So first, I want to extend a hearty thank you to Anthony for joining us today. Anthony, thank you.
ANTHONY WILSON: Yeah, thank you very much, Joan. Greatly enjoyed the conversation and hope it's useful to our audience.
JOAN PORCARO: And thank you, Omar, as well for joining us today and bringing your expertise to the table.
OMAR AL-SHAHERY: Thank you very much, Joan. Thank you for having us today. I really appreciate it. Very good questions, and I hope what we said was useful to the people who heard them.
JOAN PORCARO: That's it for today's episode of WTW Vital Signs. And to our listeners, thank you for spending part of your day with us. If you found this information helpful, please follow the show on YouTube, Apple, or Spotify and share it with any of your fellow risk management professionals who might enjoy it too. I'm Joan Porcaro and I look forward to being with you again next time on future WTW Vital Signs podcast.
SPEAKER: Thank you for joining us for this WTW podcast featuring the latest thinking on the intersection of people, capital, and risk. WTW hopes you found the general information provided in this podcast informative and helpful. The information contained herein is not intended to constitute legal or other professional advice, and should not be relied upon in lieu of consultation with your own legal advisors.
In the event you would like more information regarding your insurance coverage, please do not hesitate to reach out to us. In North America, WTW offers insurance products through licensed entities, including Willis Towers Watson Northeast, Incorporated in the United States, and Willis Canada, Incorporated in Canada.
Disclaimer
WTW hopes you found the general information provided here informative and helpful. The information contained herein is not intended to constitute legal or other professional advice and should not be relied upon in lieu of consultation with your own legal advisors. In the event you would like more information regarding your insurance coverage, please do not hesitate to reach out to us. In North America, WTW offers insurance products through licensed entities, including Willis Towers Watson Northeast, Inc. (in the United States) and Willis Canada Inc. (in Canada).
Podcast host
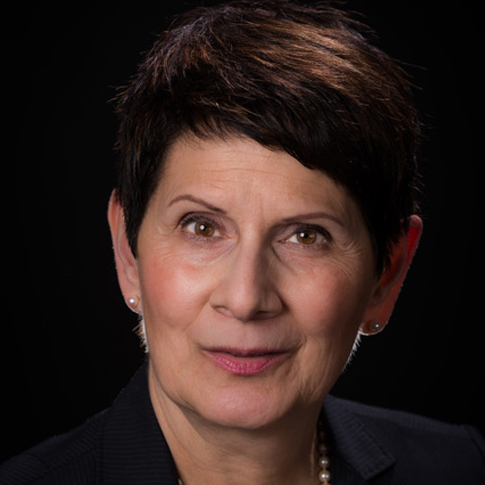
Joan Porcaro
Senior Vice President, Risk Services - Healthcare
Joan Porcaro
Senior Vice President, Risk Services - Healthcare